
Compliance
The Compliance section shows how well your AI agents meet the regulatory and industry standards your organization is accountable to letting you track control pass/fail status across frameworks like HIPAA, GDPR, SOC 2, and EU AI Act from a single page.
About compliance
Compliance gives you a framework-level view of your agent fleet's regulatory standing. Agent Identity Security continuously evaluates your agents against the compliance frameworks you have enabled and maps detected posture issues to specific controls within those frameworks. When an agent violates a control, Agent Identity Security flags it here so your compliance team can see exactly which controls are failing, which agents are responsible, and what needs to be fixed.
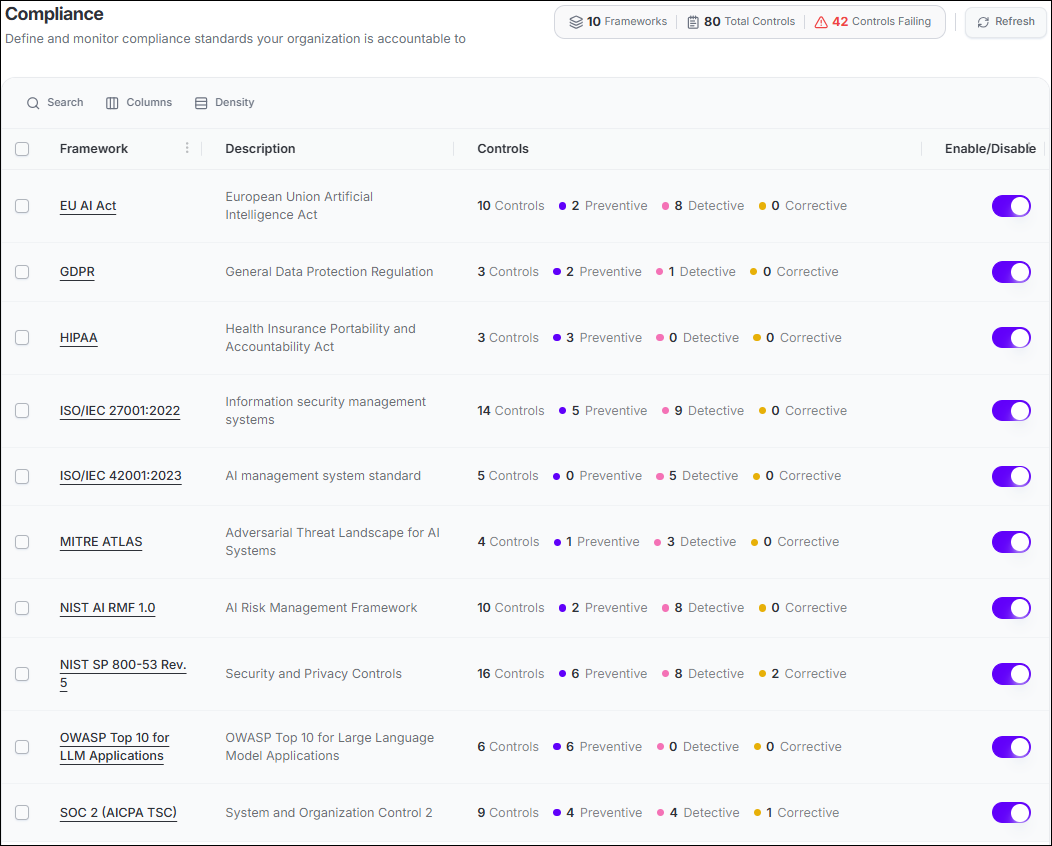
Page header summary
Three numbers in the page header give you an immediate read of your compliance posture:
| Badge / link | What it shows | What it does when selected |
|---|---|---|
| Frameworks | The total number of compliance frameworks configured in Agent Identity Security for your organization. | Display-only. Does not filter. |
| Total Controls | The total number of compliance controls mapped across all currently enabled frameworks. | Navigates to the Compliance Controls page showing every control. |
| Controls Failing (shown in red) | The number of controls currently failing because one or more agents are in violation. A red color signals that action is required. | Navigates to the Compliance Controls page pre-filtered to failing controls only your immediate remediation list. |
Frameworks list
The main table on the Compliance page shows every framework configured in Agent Identity Security. Each row has four columns:
| Column | What it shows |
|---|---|
| Framework | The short name of the standard, displayed as a selectable link. Selecting the name opens the Compliance Controls page pre-filtered to that framework's controls only. |
| Description | The full official name of the standard for example, "General Data Protection Regulation" for GDPR, or "Health Insurance Portability and Accountability Act" for HIPAA. |
| Controls | A breakdown of how many controls this framework contributes, split into three types: Preventive (stop a violation from happening), Detective (identify when a violation has occurred), and Corrective (fix a detected violation). |
| Enable / Disable | A toggle switch. When on (colored), the framework is active and its controls count toward the Controls Failing total. When off (grey), the framework is disabled its controls are hidden from monitoring but not deleted from Agent Identity Security. |
Supported frameworks
| Framework | Full name | What it covers |
|---|---|---|
| EU AI Act | European Union Artificial Intelligence Act | Accuracy, cybersecurity, post-market monitoring, and transparency obligations for AI systems operating in the European Union. |
| GDPR | General Data Protection Regulation | Data integrity, confidentiality, and security of processing for personal data belonging to EU residents. |
| HIPAA | Health Insurance Portability and Accountability Act | Transmission security and technical safeguards for protected health information in the United States. |
| ISO/IEC 27001:2022 | Information security management systems | Access control, asset management, communications security, and information security policies across your organization. |
| ISO/IEC 42001:2023 | AI management system standard | AI-specific governance, risk assessment, and lifecycle management requirements. |
| MITRE ATLAS | Adversarial Threat Landscape for AI Systems | Threats specific to AI systems, including adversarial attacks, model manipulation, and supply-chain integrity. |
| NIST AI RMF 1.0 | AI Risk Management Framework | AI risk identification, assessment, and response across the full AI system lifecycle. |
| OWASP Top 10 LLM | OWASP Top 10 for Large Language Model Applications | The most common LLM-specific vulnerabilities: Prompt Injection, Sensitive Information Disclosure, and related risks. |
| SOC 2 | Service Organisation Control 2 | Data transmission protection and system access controls for service organisations. |
| NIST 800-53 | NIST Special Publication 800-53 | Access enforcement and security categorization controls for federal information systems. |
Common difficulties
| Difficulty | What to do |
|---|---|
| I enabled a new framework and the Controls Failing count jumped significantly. | This is expected. Enabling a framework surfaces all the controls you were already failing under that standard they were just not being tracked before. Work through the new failures using the remediation workflow in the Controls page. |
| A framework my organization needs is not in the list. | The frameworks available in Agent Identity Security are configured by AppViewX. Contact your AppViewX account team to request that a specific framework be added to your tenant. |
| I disabled a framework by mistake. | Select the Enable/Disable toggle in that framework's row on the main Compliance page to re-enable it. The framework's controls are restored to monitoring immediately. |
