
Apache (Windows)
-
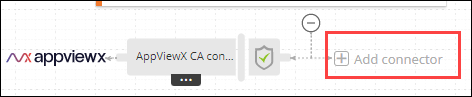
On the certificate holistic view, click Add
Connector.
-
Enter the General Information for the connector.
Table 1. Field descriptions for the connector General Information Field Description *Category From the dropdown list, select Server. If the certificate being pushed was enrolled with CSR generation at endpoint, this field is auto populated with the category selected at the time of certificate enrollment.
*Vendor From the dropdown list, select Windows Apache. If the certificate being pushed was enrolled with CSR generation at endpoint, this field is auto populated with the vendor selected at the time of certificate enrollment.
*Connector Name Enter a name for this connector to be able to identify it later. Tip: AppViewX recommends naming connectors according to use cases so they are easily distinguishable.Description Enter any additional details you want to record for this connector. Based on the information entered here, the SSL templates section is populated with the list of available Windows Apache devices already onboarded in AppViewX. -
To select the device(s) to which the certificate will be pushed, under SSL
templates, from the list of Available Devices, click
 .
The Selected devices list is updated automatically.
-
Enter the Certificate Details.
Table 2. Field descriptions for the Certificate Details Field Description Use Existing Configuration Certificate and key will be pushed to the virtual host section of the configuration file associated with the selected profile, using the existing configuration assigned to that profile. This ensures that the existing configuration remains unchanged. Because the certificate is deployed through the existing certificate configuration, no additional binding is required. Once the push operation is complete, the selected Service Action will be applied. *Certificate Type From the dropdown list, select the file type of the certificate to be pushed. *Certificate Location Enter the path to the location on your local system where the certificate file to be pushed is stored. *Key Location The private key associated with a certificate is stored in a key file. In the Key directory field, enter the path to the location on your local system where the private key file for the certificate to be pushed is stored.
Push Root and Intermediate Certificates To push the root and intermediate certificates, along with the end certificate, select this checkbox. Note:- The application automatically adapts certificate
deployment based on the Apache SSL configuration.
If
SSLCertificateChainFileis configured in the Apache configuration, the server certificate and certificate chain are deployed separately. If it is not configured, the certificate chain is bundled with the server certificate and deployed throughSSLCertificateFile. - When this option is disabled, the application updates only the SSLCertificateFile directive.
Certificate Chain File Location Note: This field is displayed when Push Root and Intermediate Certificates is enabled.Enter the path of the target location for the certificate chain file:- Legacy configuration: When
SSLCertificateChainFileis present in the Apache SSL configuration file, the intermediate and root certificates are bundled and deployed to the specified Certificate Chain File Location. - New configuration: When
SSLCertificateChainFileis not present in the Apache SSL configuration file, any value specified for Certificate Chain File Location is ignored.
Root CA Certificate File Location Note: This field is displayed when Push Root and Intermediate Certificates is enabled.Enter the path of file location for deploying the root CA certificate:- If a path is provided in Root CA Certificate
File Location, the root CA certificate content
is appended to the existing file referenced by the
SSLCACertificateFiledirective, only if the same certificate content is not already present in the root CA bundle.
Service Action Select the service action to be executed after certificate deployment: - None: No service action is performed after certificate deployment.
- Reload: Reloads the Apache service to apply the updated certificate without interrupting existing connections.
- Restart: Restarts the Apache service after certificate deployment.
Note: The default Service Action is inherited from the Global Device Settings. To view or update the default, go to: Menu > CLM > ADMINISTRATION > Device Management > Server > Device Settings.Private Key in Device If the private key associated with the certificate being pushed has been stored on a hardware device, select this checkbox. - The application automatically adapts certificate
deployment based on the Apache SSL configuration.
If
-
Enter the Push Details.
Table 3. Field descriptions for the Push Details Field Description *Script Location Script files are commonly used to perform certain tasks required to be completed before and/or after a certificate is pushed to the target system. The script to be run before the certificate is pushed is called a pre-push script and the script to be run after the push is called a post-push script.
From the following options, select the location of the script file(s):
- In AppViewX
- In Device
Pre - Push Script File Name Enter the file name of the pre-push script. Important: Read the pre and push script usage instructions here.Pre - Push Script File Path This field is displayed when Script Location = In Device. Enter the location on your local system where the pre-push script file is stored.Important: Read the pre and push script usage instructions here.Post - Push Script File Name Enter the file name of the post push script.Important: Read the pre and push script usage instructions here.Post - Push Script File Path This field is displayed when Script Location = In Device. Enter the location on your local system where the post-push script file is stored.Important: Read the pre and push script usage instructions here.Push Automatically To automatically push the certificate after it is renewed/reissued to the target system, enable this checkbox. Note: The auto push feature for a certificate works only if enabled for the certificate application connector as well the associated certificate group. To enable this feature at the certificate group level, refer the instructions here. -
Click Save.
The connector is displayed on the certificate holistic view.
What's Next
- To push a server certificate to a device, see Pushing a Server Certificate to a Device.
