Microsoft Intune
Microsoft Intune is a cloud-based endpoint management solution that provides mobile device management (MDM). Intune Win32 application management enables administrators to pre-package 32-bit and 64-bit Windows applications into the .intunewin format, configure custom installation scripts, enforce hardware and OS prerequisites, and monitor deployment status across enterprise endpoints.
Deploying Agent Identity Security Code Guardian as a Win32 application ensures consistent, silent enrollment across your organization's managed Windows devices.
- Download the required installation package
(Invoke-BootstrapEnrollment.intunewin) and custom
detection script (Detect-CodeGuardian.ps1).
Downloading the MDM Package for Intune.
To download the Intune MDM package, please follow these steps:- Navigate to the page in your platform.
- Select the vendor of your choice (e.g., Claude Code, Cursor,
GitHub Copilot, etc.).
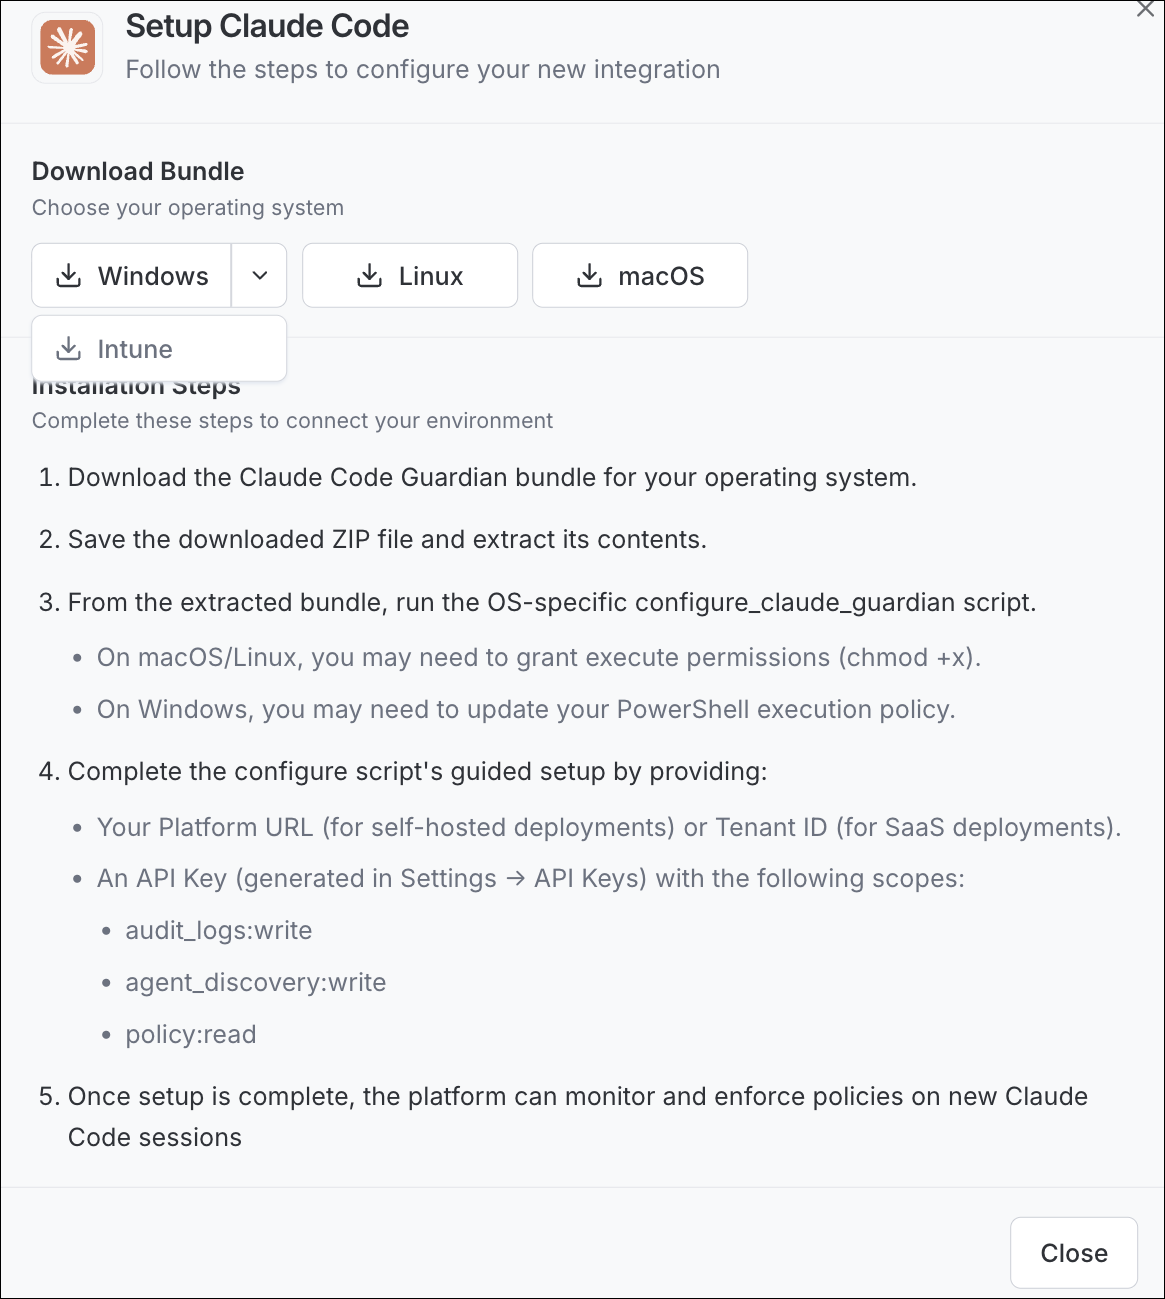
- In the Setup dialog that appears, click the dropdown arrow next to the Windows button under Download Bundle.
- Click Intune from the dropdown menu to download the MDM package.
Note: The Intune MDM package is a unified package that supports all coding agent integrations. While the package is available for download from each individual coding agent integration (such as Claude Code, Cursor, or GitHub Copilot), you don't need to install a separate package for each one. Deploy the package once to enable discovery across all supported coding agents. - Generate an active Bootstrap Token from the Agent Identity Security Platform. For step-by-step instructions, see Generate Bootstrap Token in AppViewX Agent Identity Security.
- An active Microsoft Intune administrator account with permissions to add, configure, and assign Win32 applications (such as Intune Administrator or Global Administrator).
- Outbound HTTPS network connectivity on port 443 from all target Windows endpoints to the Agent Identity Security Platform (https://ais.appvx.com). Verify that firewalls, VPNs, web proxies, and TLS inspection rules allow this traffic.
Create a Win32 Application in Microsoft Intune
- Sign in to the Microsoft Intune admin center.
- In the left navigation pane, select .
- Select + Add.
- In the Select app type pane, under Other, select Windows app (Win32), and then select Select.
-
On the App package file pane, upload the deployment
package:
- Select the browse icon and locate the Invoke-BootstrapEnrollment.intunewin file.
- Select OK to upload the package.
-
On the App information tab, enter the application
metadata, and then select Next:
- Name: Enter a unique, descriptive name (for example, Agent Identity Security Code Guardian).
- Description: Enter a summary of the application's purpose.
- Publisher: Enter AppViewX.
- App Version: Enter the package version (for example, 0.1.0).
- Category: Select relevant organizational categories (such as Productivity or Development & Design).
- Developer: Enter the responsible team or administrator alias.
Tip: Optional fields such as Information URL, Privacy URL, and Logo can be configured according to your organization's branding guidelines. -
On the Program tab, configure the installation and
removal commands, and then select Next:
-
Install command: Enter the following PowerShell command (substitute placeholders with your environment details):
powershell.exe -ExecutionPolicy Bypass -File Invoke-BootstrapEnrollment.ps1 -ApiBaseUrl "https://ais.appvx.com/api/v1" -TenantId "YOUR_TENANT_SUBDOMAIN" -TenantSubdomain "YOUR_TENANT_SUBDOMAIN" -BootstrapToken "YOUR_BOOTSTRAP_TOKEN" -Plugins "claude,cursor,copilot"
Example:
powershell.exe -ExecutionPolicy Bypass -File Invoke-BootstrapEnrollment.ps1 -ApiBaseUrl "https://ais.appvx.com/api/v1" -TenantId "acme" -TenantSubdomain "acme" -BootstrapToken "bt_xxxxxxxxxxxxxxxx_xxxxxxxxxxxxx" -Plugins "claude,cursor,copilot"
-
Uninstall command:
ais-code-guardian.exe /quiet --uninstall
- Installation time required (mins): 5
- Allow available uninstall: Yes
- Install behavior: System
- Device restart behavior: No specific action
- Device restart behavior return codes: Retain default values (0 = Success, 1 = Failed, 1618 = Retry, 1641 = Hard reboot, 3010 = Soft reboot).
-
-
On the Requirements tab, define the endpoint
prerequisites, and then select Next:
- Operating system architecture: Select 64-bit.
- Minimum operating system: Select Windows 10 1607 (or later).
Note: Leave physical memory, disk space, and CPU requirements empty unless mandated by specific hardware baselines. -
On the Detection rules tab, configure custom script
detection, and then select Next:
- In the Rules format list, select Use a custom detection script.
- In the Script file field, upload Detect-CodeGuardian.ps1.
- Set Run script as 32-bit process on 64-bit clients to No.
- Set Enforce script signature check and run script silently to No (unless code signing is strictly enforced in your tenant).
-
On the Assignments tab, assign the deployment groups,
and then select Next:
Under Required, select + Add group and choose the target Microsoft Entra ID device group.
-
On the Review + create tab, verify all configuration
parameters, and then select Save (or
Create).
The Win32 application is created, uploaded to Intune storage, and queued for deployment to the assigned endpoints.
Verify Deployment
- Intune Management Status: In the Intune admin center, go to and verify that target endpoints show Installed.
- Agent Identity Security Device Registration: Sign in to the Agent Identity Security Platform, navigate to Activity Logs, and verify that an event with action Device.Registration appears for the endpoint.
- Managed Agents List: In the Agent Identity Security Platform, go to Managed Agents and confirm that the target device and associated plugins are listed and active.
Uninstall Agent Identity Security Code Guardian
- Via Microsoft Intune: Remove the target device group from the Required assignment and add it under the Uninstall assignment. Intune will automatically execute ais-code-guardian.exe /quiet --uninstall.
-
Manual Uninstall (MSI): Run the following command with administrative privileges on the target endpoint:
msiexec /x ais-claude-guardian_0.1.0_x64.msi /qn